Audit-Ready Access: Automating Compliance and Governance for 2027
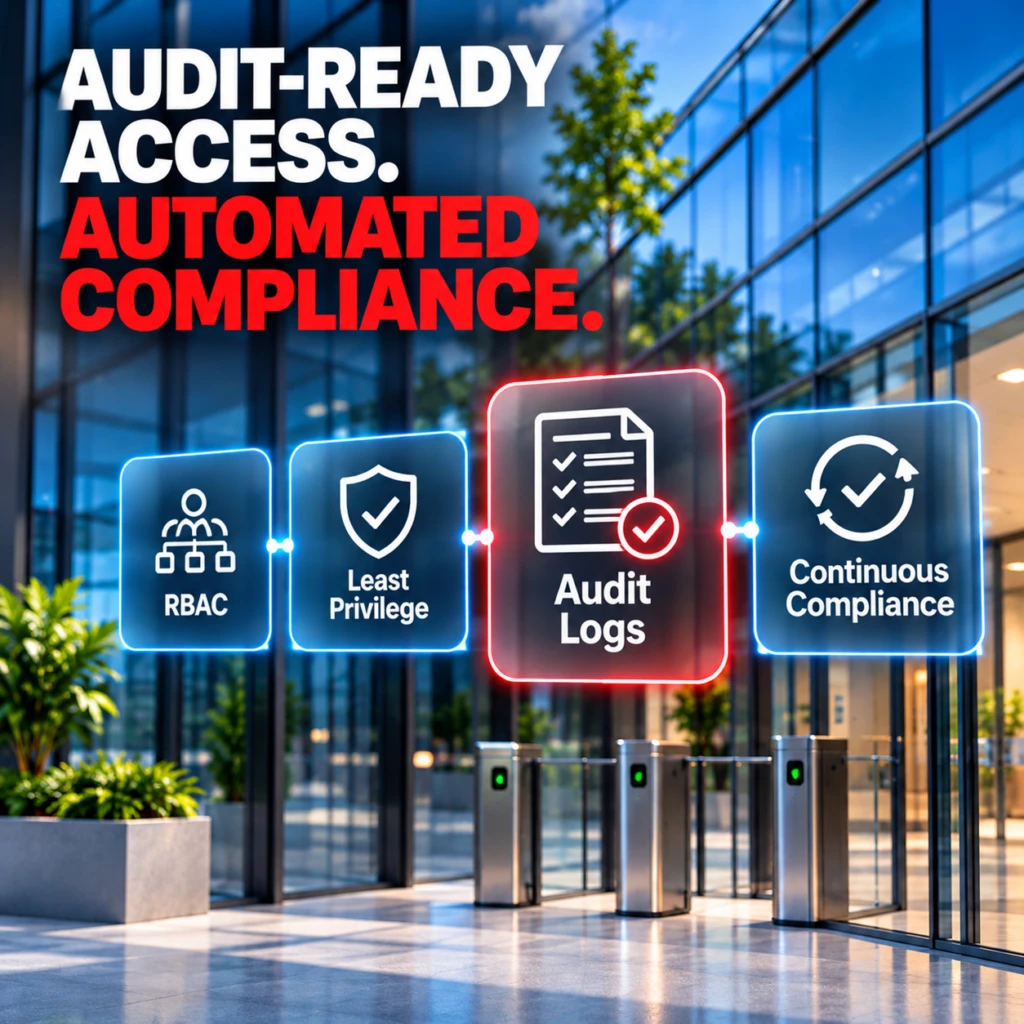
Enterprise access environments are getting more complex, not less. IT teams, security operations, facility leaders, and property managers are expected to control who can enter buildings, systems, and sensitive spaces while also proving that those controls are consistently enforced. In that environment, audit-ready access is no longer a best practice — it is an operational requirement. By 2027, organizations will need more than periodic reviews and spreadsheet-based access lists. They will need access governance automation that supports continuous compliance, produces reliable audit evidence, and reduces the manual burden on IT, security, and facilities teams. The core principles remain familiar: least privilege, role-based access control (RBAC), audit log management, and strong governance processes. What changes is the expectation that these controls should be embedded into daily operations, not added after the fact. (csrc.nist.gov) Why Audit-Ready Access Matters Now Audit readiness has traditionally been treated as a point-in-time event. Teams prepare evidence when a review, certification, or assessment is approaching, then move back to business as usual. That model creates risk because access permissions, contractor relationships, tenant needs, and staff responsibilities change constantly. Modern compliance frameworks emphasize ongoing control over access and logging. NIST guidance supports access control based on policy, role, and least privilege, while CIS Controls v8.1 specifically calls for access control management and audit log management as core safeguards. ISO/IEC 27001 and ISO/IEC 27002 also frame access control as part of a broader information security management system. (tsapps.nist.gov) For enterprise facilities and commercial real estate environments, that means the same governance discipline should apply across: employee badge access contractor and vendor access tenant-specific permissions privileged administrative access physical and logical access review processes When these controls are fragmented, audit preparation becomes expensive and error-prone. When they are automated, organizations can improve oversight while reducing manual work. What “Audit-Ready Access” Means in Practice Audit-ready access is the ability to prove, at any moment, that access is: approved appropriate to the user’s role time-bound where needed logged reviewed revoked when no longer required This is where identity governance and access governance automation become critical. A mature access program should not simply issue credentials. It should maintain an ongoing record of why access exists, who approved it, when it was last reviewed, and whether it still aligns with policy. In practical terms, audit-ready access usually includes: Defined roles and entitlementsAccess is mapped to job function, location, tenant, or operational need. Least privilege enforcementUsers receive only the minimum access necessary to perform assigned tasks. NIST defines least privilege as restricting privileges to the minimum necessary to accomplish assigned tasks. (csrc.nist.gov) Reviewable access decisionsEvery approval, change, and revocation can be traced. Audit logs and retentionEvents can be reviewed to detect, understand, or recover from attacks or policy violations. CIS explicitly identifies audit log management as a core control. (cisecurity.org) Governance workflowsAccess changes follow standardized approvals, exceptions, and recertifications. The 2027 Shift: From Periodic Reviews to Continuous Compliance The biggest shift heading into 2027 is the move from reactive compliance to continuous compliance. This does not mean replacing human oversight. It means automating the repetitive parts of governance so people can focus on exceptions, investigations, and policy decisions. Continuous compliance is especially important in environments where access changes quickly: seasonal staffing contractor rotation tenant turnover new facilities or sites hybrid work and remote administration temporary emergency access Automation helps by standardizing the workflow around access requests, approvals, renewals, and revocations. It also helps teams detect drift — for example, when a user’s access no longer matches their role or when an inactive credential remains enabled. Industry guidance supports this approach. CIS Control 6 focuses on managing access privileges, and CIS Control 8 focuses on collecting, alerting, reviewing, and retaining audit logs. NIST also emphasizes role-based and policy-driven access control. (cas.docs.cisecurity.org) The Business Case for Access Governance Automation For IT directors and enterprise security leaders, the value of automation is not just compliance. It is operational clarity. 1. Faster audit preparation When access data, approvals, and logs are centralized, teams can produce evidence faster and with less manual reconciliation. 2. Lower risk of stale access Automated recertification and expiration policies reduce the chance that old accounts or overprivileged users remain active. 3. Better accountability RBAC and approval workflows make it easier to determine who approved what, when, and under which policy. 4. More consistent enforcement Policies applied through workflows are less likely to vary by site, manager, or department. 5. Improved collaboration across teams Facilities, security, IT, and property management can work from the same governance model instead of maintaining separate spreadsheets or siloed approval paths. Key Components of an Audit-Ready Access Program 1. Role-Based Access Control RBAC assigns access based on role rather than individual preference. NIST describes RBAC as a way to manage access based on job function, and it has long been recognized as a practical model for enterprise security. (csrc.nist.gov) In commercial environments, RBAC can be used to separate: corporate administrators building operators tenant users contractors security personnel temporary visitors 2. Least Privilege Access Least privilege is foundational. If a user only needs access to a subset of doors, applications, or administrative functions, they should not have broader privileges by default. NIST and CIS both support this principle as a core access control safeguard. (csrc.nist.gov) 3. Strong Audit Logging Logs should capture access events, privilege changes, approvals, denials, and administrative actions. CIS Control 8 is explicit that audit logs should be collected, reviewed, and retained to help detect, understand, or recover from an attack. (cisecurity.org) 4. Access Review Workflows A strong governance program requires regular access reviews. These reviews should verify: whether access is still needed whether the role has changed whether the user is still active whether any exceptions exist whether high-risk access requires additional approval 5. Separation of Duties For sensitive environments, no single person should control every step of the process. NIST 800-171 discusses separation of duties, including ensuring personnel who administer access control functions do not also administer audit functions. (nvlpubs.nist.gov) How Automation Supports Compliance and Governance
The Alert Fatigue Problem: When Every Security Event Looks Urgent
Introduction A door-held-open alarm. An access-denied event. Another notification from a different building. For security operations teams, IT Directors, Facility Managers, and Commercial Property Managers, these events are part of everyday security management. But as organizations expand across more doors, users, and locations, the volume of information can quickly become overwhelming. The challenge is no longer simply receiving security alerts. It is knowing which alerts deserve attention, which events require investigation, and which notifications are part of normal building activity. When every security event looks urgent, the events that matter most can become harder to recognize. That is the alert fatigue problem. And for organizations managing increasingly complex physical security environments, more notifications do not necessarily mean better protection. What Is Security Alert Fatigue? Security alert fatigue occurs when teams receive so many notifications, alarms, and system events that it becomes difficult to consistently identify and respond to meaningful security risks. In physical access control, not every event indicates a security threat. An employee presenting an expired credential may generate an access-denied event. A door held open during a delivery may trigger an alarm. A maintenance worker accessing a restricted area outside normal hours may require investigation. Each event provides information, but not every event requires the same response. The problem begins when systems present routine activity, operational issues, and potentially serious incidents without enough context to distinguish between them. Over time, excessive notifications can create unnecessary workloads, slow investigations, and make security teams less effective. The goal should not be to eliminate security alerts. It should be to make them more meaningful. Why Modern Access Control Systems Generate So Much Information Today’s commercial buildings and enterprise facilities rely on access control systems to manage more than basic entry permissions. They support employees, tenants, contractors, vendors, visitors, and service providers across different doors, schedules, and locations. Every interaction can generate a record. Common access control events include: Access granted or denied Doors held open beyond permitted periods Forced-door alarms Credentials used outside authorized schedules Changes to access permissions Controller or communication issues Unusual activity requiring further review Individually, these events can be useful for security monitoring and auditing. Across hundreds of doors and thousands of users, however, the volume can become difficult to manage. The challenge becomes even greater when access control, video surveillance, visitor management, and other security systems operate independently. Security teams may need to switch between multiple platforms to understand what happened, where it happened, and whether action is necessary. That fragmentation can turn a simple event into a time-consuming investigation. The Hidden Cost of Too Many Security Alerts Alert fatigue is not simply an inconvenience. It can affect how effectively an organization manages security. Slower response to important incidents When operators must review large numbers of routine notifications, critical events may compete for attention with less significant activity. A forced-door alarm should not be treated with the same urgency as an employee accidentally presenting an expired credential. Without clear priorities, response times may suffer. Increased operational workload Every unnecessary investigation consumes time. Facility managers may need to contact employees, security personnel may need to review camera footage, and IT teams may be asked to troubleshoot events that could have been resolved through better system configuration. For organizations with limited security staffing, these demands can quickly become significant. Reduced visibility across multiple locations Managing one building is challenging enough. Managing a portfolio of commercial properties, corporate offices, or distributed facilities introduces additional complexity. Different schedules, tenant requirements, access policies, and operating procedures can generate inconsistent notifications across locations. Without centralized visibility, identifying recurring problems becomes more difficult. Greater risk of overlooked patterns An individual access-denied event may be harmless. Repeated denied attempts at the same restricted entrance, however, may deserve closer attention. If events are reviewed only as isolated notifications, important patterns can be harder to identify. Security teams need the ability to understand activity over time, not simply react to individual alarms. From Security Events to Actionable Intelligence Modern access control should do more than record what happens at a door. It should help security teams understand the circumstances surrounding an event. Consider two situations. In the first, a door-held-open alarm occurs during a scheduled delivery while authorized personnel are present. In the second, the same alarm occurs at a restricted entrance after business hours. The event type may be identical, but the security implications are different. Understanding that difference requires context. Useful context may include: The location of the event The time and date The credential or user involved Applicable access schedules Recent activity at the same entrance Related video footage Previous alarms or recurring patterns When this information is easier to access and interpret, security personnel can make more informed decisions. Instead of treating every notification as an isolated problem, teams can evaluate events within the broader operational environment. That is the difference between collecting security data and using it effectively. Why Video Integration Matters Access control systems provide valuable information about credentials, permissions, and door activity. Video surveillance can provide visual context that helps explain what happened. When these systems operate separately, security personnel may need to manually locate the relevant camera, identify the correct time, and compare footage with access logs. That process takes time, particularly when managing multiple facilities. Integrating access control with video management can simplify investigations by making related information easier to retrieve. For example, when a forced-door alarm occurs, security personnel may be able to review associated camera footage to determine whether the event involved unauthorized entry, a maintenance issue, or another situation. The benefit is not simply having more information. It is having the right information available when it is needed. For security operations teams, better integration can support faster investigation, more consistent responses, and improved situational awareness. How AI and Automation Are Changing Security Operations Artificial intelligence and automation are becoming increasingly important topics in physical security. Their potential value is not limited to detecting unusual activity. They can also help organizations manage growing amounts
The Hardware Trap: How Open Architecture Cures Vendor Lock-in
Enterprise security has a blind spot. For too many organizations, access control still depends on manual processes, disconnected systems, and overworked teams. That might have been manageable when one site, one badge system, and one administrator could cover everything. It is not manageable now. Today, IT Directors, Facility Managers, CRE Property Managers, Commercial Property Owners, and Security Operations teams are expected to support more users, more locations, more exceptions, and more risk — often without the staff to keep up. That is the SMB access gap. It is the gap between the security posture your organization needs and the operational reality your team has to work with. And it is exactly where enterprise security starts to break down. What the SMB Access Gap Really Means The SMB access gap is not just a staffing issue. It is a security architecture issue. When access decisions depend on manual approvals, inconsistent badge rules, siloed systems, or outdated policies, the result is predictable: too much access, too little visibility, slow revocation, weak auditability, and unnecessary exposure across people, places, and systems. That is a serious problem for lean organizations and distributed enterprises alike. It is especially risky in commercial properties and multi-site environments, where access often has to be managed across tenants, vendors, contractors, employees, and visitors. If your team is still forced to patch together access control with spreadsheets, email approvals, or legacy tools that were never built for modern governance, you are already carrying security debt. Why Enterprise Security Is Harder Without a Large IT Department Modern access control is no longer just about opening a door. It is about proving identity, enforcing policy, limiting privilege, and creating an audit trail that holds up under scrutiny. That is a lot to ask of a small team if the system was never designed to scale. The pressure usually shows up in a few familiar ways: Manual provisioning slows everything down Every new employee, contractor, or tenant request creates work. Every role change creates more work. Every offboarding event creates risk if it is not handled immediately. Siloed systems create inconsistency If physical access, identity management, and security operations live in separate places, policies drift. What is allowed in one building may not match another. What is revoked in one system may still be active in another. Visibility disappears across sites Without centralized control, it becomes difficult to answer basic questions: Who has access? To what? For how long? And under what policy? Legacy tools demand too much maintenance Older systems may still function, but they often require heavy administration, on-prem support, or workarounds that drain time from already stretched teams. Physical and digital access are no longer separate problems The modern enterprise has a cyber-physical security challenge. If identity governance is weak, physical access becomes weak. If authorization is unclear, security becomes inconsistent. That is why the SMB access gap matters. It is not just about convenience. It is about control. The Security Model That Closes the Gap The answer is not more complexity. The answer is a smarter access model built around identity, least privilege, centralized policy, and zero trust principles. That starts with one core assumption: access should never be granted simply because someone is “inside” the network, inside the building, or inside the organization. Access must be verified, limited, and continuously governed. Zero trust access control Zero trust is not a product. It is a security approach. Instead of assuming trust based on location or legacy boundaries, zero trust evaluates identity, context, and policy before access is granted. That applies to digital systems, and it increasingly applies to physical access as well. For lean teams, this matters because it shifts the model from reactive administration to governed access. The system is doing more of the work, so the team does not have to. Identity-based access control The cleanest way to scale access is to tie it to identity. That means access follows the person, not the spreadsheet. It follows role, not memory. It follows policy, not improvisation. Identity-based access control gives organizations a more reliable way to manage permissions across buildings, departments, sites, and user types. Least privilege by default If someone does not need access, they should not have it. That principle sounds simple, but it is one of the most effective ways to reduce risk. The fewer unnecessary permissions you carry, the smaller your exposure when something goes wrong. Role-based access control Role-based access control helps reduce administrative burden by grouping permissions according to job function or user category. For example: facility staff may need broad operational access, contractors may need limited, time-bound access, tenants may need access only to designated areas, executives may need elevated access to specific spaces. The point is not to overcomplicate access. The point is to make it predictable, repeatable, and enforceable. What Modern Access Control Should Look Like If your organization wants enterprise security without enterprise staffing, your access model should do five things well: 1. Centralize policy Security teams should not have to manage access rules separately for every site or department. Policy should be governed from one place. 2. Reduce manual intervention The fewer handoffs required to grant, adjust, or revoke access, the less room there is for error. 3. Support the full user lifecycle Access should be easy to assign when someone joins, update when their role changes, and remove immediately when they leave. 4. Create audit-ready visibility Security operations teams need clear logs and consistent records. If you cannot prove who had access and why, you do not really have control. 5. Scale across physical and operational environments Access control should work across office buildings, mixed-use properties, distributed teams, and evolving portfolios without forcing your staff into constant cleanup mode. That is the difference between a system that looks modern and a system that actually reduces risk. Where Commercial Property and CRE Teams Feel the Pain Most In commercial real estate and property management, access control complexity is often underestimated. You are not just managing employees.
The SMB Access Gap: Enterprise Security Without the IT Department
Enterprise security has a blind spot. For too many organizations, access control still depends on manual processes, disconnected systems, and overworked teams. That might have been manageable when one site, one badge system, and one administrator could cover everything. It is not manageable now. Today, IT Directors, Facility Managers, CRE Property Managers, Commercial Property Owners, and Security Operations teams are expected to support more users, more locations, more exceptions, and more risk — often without the staff to keep up. That is the SMB access gap. It is the gap between the security posture your organization needs and the operational reality your team has to work with. And it is exactly where enterprise security starts to break down. What the SMB Access Gap Really Means The SMB access gap is not just a staffing issue. It is a security architecture issue. When access decisions depend on manual approvals, inconsistent badge rules, siloed systems, or outdated policies, the result is predictable: too much access, too little visibility, slow revocation, weak auditability, and unnecessary exposure across people, places, and systems. That is a serious problem for lean organizations and distributed enterprises alike. It is especially risky in commercial properties and multi-site environments, where access often has to be managed across tenants, vendors, contractors, employees, and visitors. If your team is still forced to patch together access control with spreadsheets, email approvals, or legacy tools that were never built for modern governance, you are already carrying security debt. Why Enterprise Security Is Harder Without a Large IT Department Modern access control is no longer just about opening a door. It is about proving identity, enforcing policy, limiting privilege, and creating an audit trail that holds up under scrutiny. That is a lot to ask of a small team if the system was never designed to scale. The pressure usually shows up in a few familiar ways: Manual provisioning slows everything down Every new employee, contractor, or tenant request creates work. Every role change creates more work. Every offboarding event creates risk if it is not handled immediately. Siloed systems create inconsistency If physical access, identity management, and security operations live in separate places, policies drift. What is allowed in one building may not match another. What is revoked in one system may still be active in another. Visibility disappears across sites Without centralized control, it becomes difficult to answer basic questions: Who has access? To what? For how long? And under what policy? Legacy tools demand too much maintenance Older systems may still function, but they often require heavy administration, on-prem support, or workarounds that drain time from already stretched teams. Physical and digital access are no longer separate problems The modern enterprise has a cyber-physical security challenge. If identity governance is weak, physical access becomes weak. If authorization is unclear, security becomes inconsistent. That is why the SMB access gap matters. It is not just about convenience. It is about control. The Security Model That Closes the Gap The answer is not more complexity. The answer is a smarter access model built around identity, least privilege, centralized policy, and zero trust principles. That starts with one core assumption: access should never be granted simply because someone is “inside” the network, inside the building, or inside the organization. Access must be verified, limited, and continuously governed. Zero trust access control Zero trust is not a product. It is a security approach. Instead of assuming trust based on location or legacy boundaries, zero trust evaluates identity, context, and policy before access is granted. That applies to digital systems, and it increasingly applies to physical access as well. For lean teams, this matters because it shifts the model from reactive administration to governed access. The system is doing more of the work, so the team does not have to. Identity-based access control The cleanest way to scale access is to tie it to identity. That means access follows the person, not the spreadsheet. It follows role, not memory. It follows policy, not improvisation. Identity-based access control gives organizations a more reliable way to manage permissions across buildings, departments, sites, and user types. Least privilege by default If someone does not need access, they should not have it. That principle sounds simple, but it is one of the most effective ways to reduce risk. The fewer unnecessary permissions you carry, the smaller your exposure when something goes wrong. Role-based access control Role-based access control helps reduce administrative burden by grouping permissions according to job function or user category. For example: facility staff may need broad operational access, contractors may need limited, time-bound access, tenants may need access only to designated areas, executives may need elevated access to specific spaces. The point is not to overcomplicate access. The point is to make it predictable, repeatable, and enforceable. What Modern Access Control Should Look Like If your organization wants enterprise security without enterprise staffing, your access model should do five things well: 1. Centralize policy Security teams should not have to manage access rules separately for every site or department. Policy should be governed from one place. 2. Reduce manual intervention The fewer handoffs required to grant, adjust, or revoke access, the less room there is for error. 3. Support the full user lifecycle Access should be easy to assign when someone joins, update when their role changes, and remove immediately when they leave. 4. Create audit-ready visibility Security operations teams need clear logs and consistent records. If you cannot prove who had access and why, you do not really have control. 5. Scale across physical and operational environments Access control should work across office buildings, mixed-use properties, distributed teams, and evolving portfolios without forcing your staff into constant cleanup mode. That is the difference between a system that looks modern and a system that actually reduces risk. Where Commercial Property and CRE Teams Feel the Pain Most In commercial real estate and property management, access control complexity is often underestimated. You are not just managing employees.
The Zero-Infrastructure Job Site: Securing the Rotating Workforce
Commercial properties, enterprise facilities, and job sites increasingly depend on rotating workforces: contractors, vendors, service teams, temporary staff, and after-hours maintenance crews. That creates a simple but difficult problem: how do you secure people who move frequently, need time-bound access, and may not return to the same site tomorrow? The answer is not more keys, spreadsheets, or ad hoc door codes. For many organizations, the better model is a zero-infrastructure job site—a security approach that reduces on-site hardware dependence, centralizes identity-based access decisions, and supports rapid onboarding and offboarding for changing teams. This article explains how IT Directors, Facility Managers, CRE Property Managers, Property Owners, and Security Operations teams can secure a rotating workforce using modern access control, visitor and contractor management, and Zero Trust security principles. What “Zero-Infrastructure Job Site” Means A zero-infrastructure job site is not a site with no security. It is a site that minimizes the need for heavy, locally managed access infrastructure while still enforcing strong control over who can enter, when they can enter, and what they can access. In practice, that usually means: Identity-based access instead of static credentials Cloud-managed or centrally managed access control Mobile credentials or temporary credentials Time-bound permissions for contractors and vendors Continuous logging and auditability Integration with HR, vendor, and visitor workflows This aligns with Zero Trust guidance that emphasizes verifying identity explicitly, applying least privilege, and assuming breach. Microsoft’s Zero Trust guidance also notes that network firewalls and VPNs alone are no longer sufficient for modern access patterns. Why Rotating Workforces Create Security Risk Rotating workforces are operationally necessary, but they create predictable access challenges: Credentials are issued and revoked too slowly Shared door codes get reused Temporary workers accumulate unnecessary access Contractors need access to different zones on different days Facility teams lose visibility into who is on-site Offboarding becomes inconsistent across departments For physical security, the main issue is that access must be tied to the person, the role, and the time window—not to a permanent badge floating around a job site. Modern physical access control systems are designed to admit only authorized people through secured entry points and to log access for audit purposes. The Core Security Principles Behind a Zero-Infrastructure Job Site Verify identity before granting access Zero Trust frameworks recommend explicit verification of users and devices before access is allowed. Microsoft’s guidance describes verifying identities, checking device health, and applying real-time policies as core Zero Trust practices. Grant the minimum access needed Contractors should receive only the access required for their assignment. Microsoft’s Zero Trust guidance explicitly recommends least privilege access and just-in-time access for sensitive functions. Assume the site boundary is not enough A rotating workforce may be accessing the site from many entry points, devices, and vendors. Zero Trust shifts the security model away from perimeter dependence and toward continuous validation and policy enforcement. Log, review, and audit access Physical access systems should record ingress and egress, support audit trails, and integrate with security operations workflows. Microsoft’s datacenter security guidance describes electronically logged access and monitored physical access as standard controls. The Best Security Model for a Rotating Workforce A strong model for a rotating workforce usually combines five elements: Identity proofing Role-based access assignment Time-based credential expiration Centralized logging Fast offboarding This is where cloud-managed access systems and Zero Trust policy models are especially useful. Microsoft’s Zero Trust documentation emphasizes policy-based access, device validation, and least privilege. Google’s BeyondCorp model similarly highlights identity and device-aware access without relying on traditional network trust. Mobile Credentials and Temporary Access Are Better Than Shared Codes For job sites with rotating crews, mobile credentials and temporary access badges are often a better fit than shared PINs or printed codes. Why? Credentials can be issued remotely Access can expire automatically Credentials can be tied to a named user Revocation is faster Audit trails are cleaner Physical access control guidance from industry vendors and security platforms consistently frames modern PACS as identity-centered systems that can log and manage authorized entry. For property managers and security teams, this reduces the operational burden of rekeying or manually resetting access every time a vendor rotates off site. Contractor Access Control Needs Time Boundaries Contractors are not employees, and they should not be treated like permanent insiders. A strong contractor access control process should define: Who approved the request What site or zone they can enter When access starts and ends Which doors, floors, or areas are included Whether escort is required How access is revoked after the job ends Microsoft’s privileged access guidance reinforces the principle that access should be granted only at the right time, with the right approval workflow, and at an acceptable risk level. For CRE and enterprise facilities, this is especially important in mixed-use buildings, tenant floors, loading docks, equipment rooms, and after-hours maintenance environments. Visitor Management and Contractor Management Should Work Together Many organizations treat visitor management and contractor management as separate workflows. That creates gaps. A better model is a unified access workflow that can handle: Visitors Vendors Short-term contractors Cleaning crews HVAC and maintenance providers Emergency service personnel A unified system improves visibility and reduces the risk of manual exceptions. It also helps Security Operations teams answer the question, “Who is on site right now, and why?” without relying on paper logs or disconnected systems. How to Secure a Zero-Infrastructure Job Site Without Heavy On-Site Hardware A true zero-infrastructure approach reduces local complexity while keeping security strong. Common elements include: Cloud-managed access control Central administration makes it easier to manage multi-site properties, temporary workers, and offboarding. Identity and directory integration Tie access to an employee or contractor identity record so permissions are easier to update and revoke. Role-based access control Assign access based on job role, project, or vendor status rather than personal familiarity. Time-boxed credentials Set start and end dates automatically to limit exposure. Central logging and alerts Monitor use patterns, after-hours access, and unusual door activity. Policy-based device validation Where applicable, require managed devices or trusted authentication paths
Breaking the Conduit Trap: Cloud-to-Cloud Access for Older Buildings
The conduit trap is a legacy problem hiding in plain sight Older buildings were not designed for today’s security expectations. When property teams want to add cloud-based access control, they often run into the same obstacle: limited pathways for cabling, constrained risers, aging infrastructure, and expensive disruption. That is the conduit trap. For IT directors, facility managers, CRE property managers, and security operations teams, the issue is bigger than a construction headache. It is a modernization bottleneck. The building may still function, but the physical infrastructure makes it hard to move to cloud-managed access, unify identities, and reduce administrative overhead. Cloud-to-cloud access can help break that cycle by reducing dependence on new cabling runs and enabling a more flexible architecture for older buildings. In practice, this means security teams can modernize access control while working with the building they already have, rather than forcing a full rip-and-replace. Why older buildings struggle with modern access control Legacy buildings often present a mix of physical and operational constraints: limited conduit capacity outdated wiring paths aging panels and controllers fragmented security systems siloed IT and facilities ownership difficult tenant turnover and user provisioning These issues are especially painful in commercial real estate and multi-tenant environments where uptime, tenant experience, and auditability matter. Older access control systems can also become integration dead ends, making it harder to connect physical security with cloud identity workflows and broader enterprise security operations. That is why modernization is no longer just a hardware decision. It is an architecture decision. What cloud-to-cloud access means in a legacy building context “Cloud-to-cloud access” is best understood as a model where your access control environment can connect with cloud identity, cloud management, or cloud services without forcing every part of the building to be rebuilt. For older buildings, the value is straightforward: less dependence on new conduit runs easier integration with identity providers and centralized admin tools more flexible rollout by building, floor, or tenant improved visibility across sites and portfolios better alignment with cloud-first IT governance This approach matters because cloud-based systems are widely positioned as easier to manage remotely, while hybrid approaches can preserve control where it is needed most. The right architecture starts with the building, not the buzzword In older properties, the best modernization plan is usually the one that respects building constraints. A cloud-first outcome does not necessarily require a full physical rebuild. Instead, teams should evaluate: existing controller and reader infrastructure network segmentation and cybersecurity requirements tenant separation and permission models failover behavior during network outages integration points with identity and security platforms phased rollout options across occupied space This is where Zero Trust principles become relevant. NIST describes Zero Trust Architecture as an approach that assumes no implicit trust based solely on network location or asset ownership. (nist.gov) For older buildings, that is a useful mindset: do not assume a legacy corridor, riser, or on-prem system is secure just because it has always been there. Why protocol choice matters in older buildings Legacy access control systems often depend on older communication methods that were not built for today’s security environment. Industry sources note that older protocols such as Wiegand are unidirectional and unencrypted, which can create security weaknesses. Gallagher also notes that modern device communications should support stronger protections and that protocols like OSDP are part of contemporary access control ecosystems. For enterprise teams, the takeaway is simple: modernization is not only about moving software to the cloud. It is also about improving the communication layer between readers, controllers, and management systems. How to break the conduit trap without a rip-and-replace A practical modernization strategy for older buildings usually follows a phased model: 1. Assess the physical constraints Map conduit availability, panel locations, cable paths, and tenant boundaries before selecting technology. 2. Identify the integration model Determine whether the site needs fully cloud-native access, hybrid access control, or a staged migration tied to building occupancy schedules. 3. Preserve operational continuity Choose an approach that minimizes downtime and avoids large-scale tenant disruption. Gallagher’s migration guidance emphasizes careful planning, testing, and coordination to reduce disruption during upgrades. (security.gallagher.com) 4. Prioritize interoperability Select platforms that can work with existing systems during transition rather than forcing an all-at-once replacement. 5. Align IT and facilities ownership Cloud-to-cloud access works best when IT, facilities, and security operations share a common migration plan and governance model. The business value for enterprise and CRE teams For commercial property owners and CRE managers, the advantage goes beyond convenience. A better access control architecture can support: faster tenant onboarding and offboarding centralized oversight across multiple properties easier policy enforcement clearer audit trails and reporting reduced reliance on physical key management improved alignment between cyber and physical security teams For enterprise security operations, the value is similarly strategic: cloud-connected access control can reduce blind spots and support a more unified security posture. That aligns with the broader industry movement toward integrated, cloud-enabled security management. Cloud-to-cloud access is not just for new buildings One of the biggest misconceptions in the market is that cloud access control only makes sense in modern, ground-up construction. In reality, older buildings may benefit even more because they are the ones most constrained by infrastructure. If you manage a legacy property, the right question is not “Can we rebuild the building?” It is “How do we modernize securely, with minimal disruption, and without trapping ourselves in the conduit problem?” That is the core promise of cloud-to-cloud access: it helps older buildings join a modern security architecture without waiting for a full renovation cycle. Where Millennium fits For organizations navigating legacy infrastructure, the goal is to bridge the gap between the building you have and the secure, cloud-connected environment you want. Millennium Ultra and the broader Millennium Group approach are designed to help enterprise teams modernize access control in a way that is practical, security-minded, and built for real-world property constraints. If your portfolio includes older buildings, cloud-to-cloud access may be the path that finally breaks the conduit trap. Conclusion: modernize
Portfolio Convergence: Scaling Unified Security Across Distributed Franchises
Distributed franchises and multi-site portfolios face a familiar challenge: how do you maintain consistent security when every location operates a little differently? One site may have upgraded access control. Another may still rely on legacy video systems. A third may use local workarounds that were never designed to scale. Over time, that fragmentation creates operational drag, inconsistent policy enforcement, and security blind spots that become harder to manage as the portfolio grows. That is where portfolio convergence comes in. Portfolio convergence is the move from isolated, site-by-site security systems to a unified operating model that supports centralized oversight, standardized policies, and scalable administration across distributed franchises. For IT Directors, Enterprise Facility Managers, Commercial Property Owners, CRE Property Managers, and Enterprise Security Operations teams, this is no longer a nice-to-have. It is the foundation for scalable security operations. What portfolio convergence means in practice At its core, portfolio convergence is about aligning people, policies, and technology across every location in the portfolio. Instead of managing each site as its own security island, your organization defines a common security baseline and applies it across the enterprise. That baseline usually includes: centralized access control policies unified video surveillance management standardized identity and credential workflows consistent alarm and incident response procedures common reporting and audit practices The goal is not to make every property identical. The goal is to make every property manageable within the same security framework. Why fragmented security does not scale Legacy security environments often grow organically. A new site gets its own hardware. A local team selects a different vendor. An acquired property brings in another system. Before long, the portfolio contains a mix of platforms, processes, and access policies that are difficult to govern from the center. That kind of fragmentation creates real operational problems: Inconsistent access policies across properties Limited portfolio-wide visibility into incidents and activity Manual administration for IT and security teams Siloed video and access data that slows investigations Harder onboarding for new sites, tenants, employees, and vendors When security is fragmented, every change takes longer. Every audit takes more effort. And every incident requires more coordination. The case for unified security across distributed franchises A unified security model gives enterprise teams a way to manage multiple sites from one strategic framework while still allowing local operations to function smoothly. That matters because distributed franchises need both control and flexibility. Corporate teams need visibility, consistency, and policy enforcement. Site managers need systems that are practical, repeatable, and easy to operate. Unified security helps bridge that gap by bringing key functions together: 1. Centralized access control Access control becomes easier to govern when policies, credentials, and permissions are managed consistently across the portfolio. That improves accountability and reduces the risk of access drift between locations. 2. Unified video surveillance When video management is standardized, security teams can investigate events faster, compare activity across sites, and maintain a consistent evidence trail. 3. Shared identity and policy logic A converged approach supports role-based access, credential lifecycle management, and policy enforcement tied to organizational standards rather than local preference. 4. Better operational visibility Portfolio-level oversight makes it easier to identify recurring issues, spot anomalies, and allocate resources where they are needed most. Zero trust principles belong in physical security too As organizations modernize, many are applying zero trust thinking to physical security operations as well. At a practical level, that means verifying access rather than assuming trust based on location, legacy permissions, or network proximity. It also means enforcing least privilege, limiting standing access, and maintaining strong auditability. For distributed franchises, that approach is especially valuable because it reduces reliance on site-specific exceptions. Instead of assuming every local environment is equally trusted, enterprise teams can define policy once and apply it consistently. This is particularly important when physical security systems are connected to broader IT infrastructure, identity systems, or cloud-managed platforms. What IT Directors should focus on For IT leaders, portfolio convergence is primarily an architecture and governance issue. The most effective programs start with standardization and interoperability. Key priorities include: identity-based access policies secure credential and account management standardized device onboarding network segmentation where appropriate central logging and audit visibility integration with enterprise identity and security processes The objective is to reduce complexity without losing control. A converged environment should make security easier to manage, not harder. What Enterprise Facility Managers need Facility teams are often responsible for the daily reality of security operations. They need systems that are consistent, intuitive, and resilient across locations. A converged portfolio helps facilities teams by: reducing vendor-specific workflows simplifying site onboarding making procedures easier to train and repeat improving coordination between local and corporate teams supporting faster response to incidents and service issues When systems are standardized, facilities teams spend less time troubleshooting and more time operating. What CRE Property Managers should prioritize For Commercial Real Estate and property management teams, security is about more than protection. It also affects tenant confidence, operational consistency, and asset perception. A fragmented security model can create uneven tenant experiences and make it harder to demonstrate operational maturity across the portfolio. Unified security supports CRE teams by enabling: consistent access policies clearer incident response procedures stronger portfolio oversight better accountability for vendors, contractors, and visitors a more predictable experience across properties That consistency matters when your portfolio includes multiple asset types, multiple stakeholders, and multiple operational models. What Enterprise Security Operations teams gain Security operations teams need speed, context, and visibility. When access events, alarms, and video are disconnected, investigating an incident can become a time-consuming manual process. When those systems are unified, operators can move faster and work with better context. A converged security model can support: faster incident correlation better event investigation reduced alert fragmentation clearer escalation paths stronger audit readiness In a distributed portfolio, those gains compound quickly. Common mistakes organizations make during convergence Portfolio convergence is not just a technology project. It is a governance and operational change effort. Common mistakes include: Treating every site as a special case Too many
Access as Infrastructure: Connecting Doors to HVAC and Desk Bookings
Modern buildings are under pressure from two directions at once: tighter security expectations and more flexible workplace demands. If your doors, HVAC, and desk booking systems still operate in separate silos, you are carrying unnecessary risk, unnecessary friction, and unnecessary operational cost. That is the core problem, access as infrastructure solves. Instead of treating physical access as a standalone function, this model connects identity, doors, room and desk reservations, and building operations into one coordinated framework. For IT directors, enterprise facility managers, commercial property owners, CRE property managers, and security operations teams, that shift matters. It improves governance, sharpens visibility, and helps the building respond to real-world use instead of static assumptions. Why access as infrastructure matters now The modern workplace is no longer fixed. Hybrid schedules, shared spaces, rotating tenants, contractors, and visitors have made static access models harder to defend and harder to manage. At the same time, enterprises are expected to operate under a Zero Trust mindset, where access is granted based on identity, policy, and context rather than broad trust. That is where access as infrastructure becomes valuable. It creates a foundation where: door access follows identity and policy desk booking reflects actual workspace intent HVAC responds more intelligently to occupancy and usage security teams gain better auditability facilities teams gain better operational control IT can reduce fragmentation across systems The goal is not to force every system into one platform. The goal is to make them work together securely. The problem with disconnected systems When access, facilities, and workplace tools do not talk to each other, each team ends up managing a partial version of the truth. Security may know who opened a door. Facilities may know which zones are being conditioned. Workplace teams may know who reserved a desk. But if those signals are never connected, your organization loses the context needed to enforce policy, reduce waste, and respond quickly to exceptions. That creates predictable problems: users keep access longer than they should manual exceptions pile up desk reservations do not align with physical access HVAC runs without clear occupancy context audit trails are harder to interpret IT and facilities remain trapped in separate operational models In enterprise environments, those gaps are not just inefficient. They are risk multipliers. Doors are the enforcement point Doors are where policy becomes real. A user may exist in an identity system, a reservation platform, and a facilities database, but the access decision ultimately happens at the door. That is why modern access control needs to be secure, auditable, and interoperable. A strong access architecture should support: role-based access control schedule-based permissions audit logs for access events mobile or credential-based entry directory integration lockdown and emergency response workflows scalable administration across many doors and sites Where possible, organizations should prefer established industry standards and well-documented protocols rather than closed, isolated implementations. For example, the Security Industry Association’s Open Supervised Device Protocol, or OSDP, is widely used in access control environments to improve secure communication between readers and controllers. That kind of interoperability matters when you are modernizing legacy infrastructure. HVAC should not be blind to occupancy HVAC is one of the largest operational systems in a building, and it should not be managed in isolation from how the space is actually used. When HVAC is disconnected from access and booking systems, buildings often heat, cool, and ventilate space without enough context. A reserved desk does not always mean the space is occupied. A badge event does not always mean a person is staying for the day. But when workplace data, occupancy signals, and access policy are considered together, facility teams can make more informed decisions. That does not mean access control should directly drive mechanical systems in a simplistic way. It means HVAC strategy should be informed by occupancy-aware data where appropriate, with clear governance and risk controls. In enterprise environments, deliberate integration is better than brittle automation. Doors are the enforcement point Doors are where policy becomes real. A user may exist in an identity system, a reservation platform, and a facilities database, but the access decision ultimately happens at the door. That is why modern access control needs to be secure, auditable, and interoperable. A strong access architecture should support: role-based access control schedule-based permissions audit logs for access events mobile or credential-based entry directory integration lockdown and emergency response workflows scalable administration across many doors and sites Modern access control environments increasingly rely on secure communication protocols and open standards to improve interoperability between readers and controllers. The Security Industry Association’s Open Supervised Device Protocol (OSDP) is one example adopted across the industry when modernizing legacy infrastructure. Choosing well-documented standards and interoperable technologies can help organizations reduce complexity and better prepare for future system integration. What enterprise buyers should expect from a connected architecture Different stakeholders care about different outcomes, but they all want the same thing: less fragmentation and more control. IT Directors IT needs fewer disconnected tools, cleaner identity integration, and systems that can be managed without creating shadow workflows. Access platforms should fit into enterprise identity governance and support secure administration at scale. Enterprise Facility Managers Facilities need occupancy-aware operations, less manual intervention, and better alignment between space usage and building systems. When access and booking systems are coordinated, facility planning becomes more accurate. Commercial Property Owners and CRE Property Managers Property leaders need flexibility across tenants, suites, and common areas. They also need scalable operations that support changing occupancy without sacrificing security or visibility. Enterprise Security Operations Teams Security needs clear audit trails, enforceable policy, and tools that support incident response. Access systems should help security teams see what happened, when it happened, and who was involved. The architecture principles that matter A modern access-as-infrastructure model should be built on a few practical principles. 1. Identity first Access should follow the user’s identity lifecycle. Onboarding, transfers, and offboarding should drive permissions, not manual lag. 2. Least privilege Users should only have access to the spaces, times, and functions they
Video Convergence: Unify Cameras and Doors on One Timeline | Enterprise Security
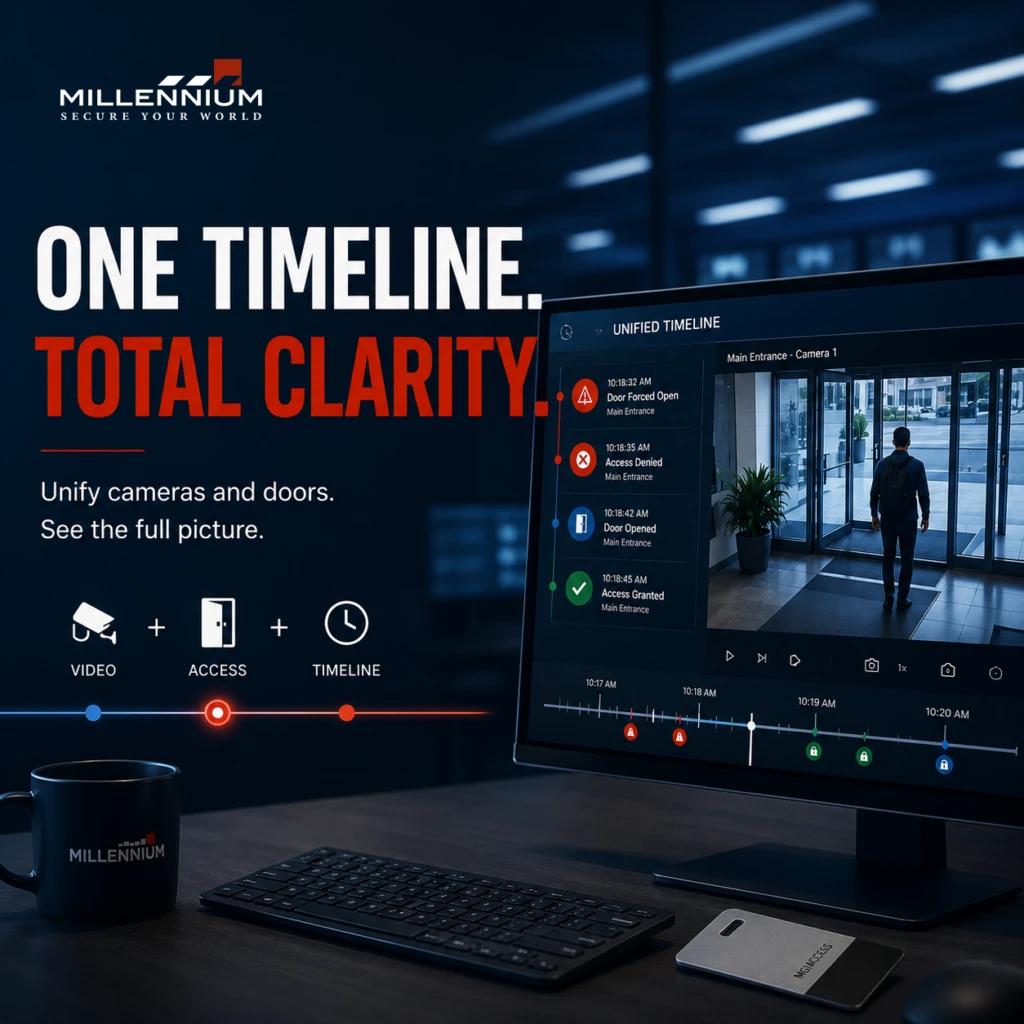
When cameras, doors, and access events live in separate systems, your security team is forced to reconstruct incidents the hard way. Operators jump between platforms, match timestamps manually, and try to piece together what happened before, during, and after an event. That fragmentation slows investigations and creates blind spots for IT, facilities, and security operations. Video convergence solves that problem by bringing video surveillance, access control integration, and event context into one operational timeline. Open standards such as ONVIF explicitly support integration between physical access control systems and video surveillance systems, which is why unified workflows have become such a practical enterprise requirement. (onvif.org) What Is Video Convergence? Video convergence is the alignment of camera footage, door events, and related security data into a single investigation workflow. Instead of treating the video management system and the access control platform as separate tools, convergence lets operators move from a door event to the relevant camera view without losing context. That is the core value of a unified security timeline: one sequence of evidence, not multiple disconnected logs. ONVIF’s access control specifications are designed to enable integration with video cameras and video monitoring systems, which supports this kind of workflow. (onvif.org) For enterprise buyers, that usually maps to these high-intent search themes: unified security timeline video and access control integration camera and door event correlation enterprise video surveillance and access control incident investigation workflow physical security convergence single-pane-of-glass security operations access control video integration Those phrases reflect clear search intent: buyers want fewer silos, faster investigations, and better operational control. (onvif.org) Why Cameras and Doors Belong on the Same Timeline Security events rarely happen in isolation. A badge swipe, a door forced-open alert, a door held-open condition, or an after-hours entry attempt usually has a corresponding camera trail. When those records are separated, your team loses time and context. When they are unified, the team can review the door event and the relevant footage in sequence. That matters because modern video systems increasingly support timeline-based retrieval and event reconstruction. Patent literature in this area shows long-standing industry interest in storing and retrieving video events in timeline format, with metadata used to index and search video more efficiently. (patents.google.com) In plain terms: one timeline means faster answers. The Operational Cost of Disconnected Systems Disconnected systems create friction in three places. 1. Investigations take longer If an operator has to open one interface for video and another for access events, every incident becomes a manual reconciliation exercise. That is exactly the kind of workflow unified systems are meant to reduce. Timeline-based retrieval and metadata-driven search are widely described in security video systems because they help users move from raw footage to relevant events faster. (patents.google.com) 2. Response depends on memory, not process When the camera view is not automatically tied to the door event, response quality depends on whether the operator remembers which camera covers which entry point. Unified workflows reduce that dependency by placing the event and the evidence in the same view. ONVIF’s access control and video integration standards exist to support that exact type of interoperability. (onvif.org) 3. IT and facilities stay siloed In many enterprises, IT owns identity, network governance, and infrastructure, while facilities owns the doors, readers, and physical response. Without a shared timeline, both teams see only part of the incident. This is where convergence supports a more modern cyber-physical operating model aligned with centralized control and standardized integrations. (onvif.org) What a Unified Video and Door Timeline Should Do A true enterprise-grade unified timeline should do more than display clips. It should support investigation and response with capabilities like: video playback linked to access events door event correlation with nearby camera footage searchable timelines across multiple cameras floorplan or map-based context support for multi-site operations role-based permissions and auditability standards-based interoperability for physical security systems (onvif.org) Some modern systems also support map-based unified timelines and multi-camera event reconstruction, which shows how the market is moving toward faster event review instead of manual scrubbing. How to Evaluate a Unified Security Platform Before you commit to a platform, evaluate it through the lens of operations. Ask: Does it unify video and access control natively or through weak point-to-point links? Can operators move from a door alert to relevant footage immediately? Does it support multi-site administration? Does it align with open standards such as ONVIF for video and access control interoperability? Can IT govern users, credentials, and permissions cleanly? Can security teams use it without constant context switching? (onvif.org) If the answer is no, you may have “integration” on paper, but not in practice. Why This Matters for IT, Facilities, and Security Operations For IT Directors, video convergence reduces system sprawl and supports cleaner governance across security infrastructure. For Enterprise Facility Managers and CRE Property Managers, it improves visibility at lobbies, loading docks, parking areas, tenant entrances, and restricted zones. For Enterprise Security Operations teams, it shortens the path from alert to action by tying the door event to the right footage in one place. That reduces the friction between detection, verification, and response. (onvif.org) The Bottom Line Video convergence is not just a feature. It is an operational strategy. When your cameras and doors live on one timeline, your team spends less time reconciling systems and more time responding to events. That shift is especially valuable in enterprise environments where security, IT, and facilities all need the same truth at the same time. Standards such as ONVIF show that the industry has already moved toward interoperable integration between access control and video surveillance. (onvif.org) If your current stack still forces your team to assemble incidents manually, it may be time to move from disconnected tools to a unified security model. Start by mapping where your cameras and doors still operate in silos. Then design the timeline first. Millennium is a scalable, hosted, access control platform that services any type of real estate. Our cloud-based solution allows managers and tenants to efficiently manage their physical security from anywhere while enhancing
Identity Convergence: Syncing Access Control with Active Directory
Enterprise security breaks down fastest at the handoff points: IT owns identity, facilities owns doors, and security ops owns risk. When those systems do not share a common identity foundation, you get duplicate records, delayed deprovisioning, inconsistent access decisions, and too much manual work during onboarding, offboarding, and role changes. That is the core problem identity convergence solves. By syncing access control with Active Directory and enterprise identity management systems, organizations can create a more unified identity layer across digital and physical environments. Instead of managing people in disconnected silos, IT and security teams can align identity lifecycle events, enforce policy more consistently, and reduce the gap between who someone is and what they can access. Why identity convergence matters now Modern enterprises are moving toward identity-centric security models. NIST’s Zero Trust guidance emphasizes identity as a key control point rather than relying only on network location or perimeter trust. In parallel, modern identity management platforms support authentication, provisioning, and directory integration through widely adopted standards such as SAML, OIDC, and SCIM. (csrc.nist.gov) For IT Directors, Enterprise Facility Managers, CRE Property Managers, and Enterprise Security Operations teams, that means the old separation between cyber and physical access is no longer sustainable. If a worker leaves, changes departments, or loses privileges, the identity source of truth should update both digital access and physical access workflows as close to real time as the architecture allows. Identity management platforms that support SCIM can automate user and group lifecycle actions, while Active Directory integration helps centralize identity management across on-premises and connected environments. What “syncing access control with Active Directory” actually means At a practical level, identity convergence means your identity provider, directory, and access control ecosystem work together through standards and integrations rather than manual exports and spreadsheet-driven administration. A typical model looks like this: Active Directory remains the authoritative directory for many legacy and on-premises systems. Microsoft documents AD’s core role in directory services and common authentication protocols in enterprise environments. (learn.microsoft.com) Enterprise identity management platforms provide centralized authentication, federation, and lifecycle orchestration across applications and directories. SCIM automates user and group provisioning, updates, and deactivation between identity providers and connected applications. SAML and OIDC provide standardized federated authentication for modern applications and services. In a converged environment, a joiner-mover-leaver event in HR or an identity management system can trigger downstream changes that update access more consistently across systems. That is the operational value of identity convergence: fewer manual handoffs, fewer orphaned accounts, and a cleaner chain of trust. Identity convergence reduces the cyber-physical gap One of the biggest risks in enterprise security is the gap between digital identity and physical access. A user may be disabled in one system while still active in another. A contractor may still appear in a badge workflow after their project ends. A role change may update application access but not physical permissions. That gap creates operational risk. Identity management platforms support centralized lifecycle management across connected systems, while Microsoft’s directory and authentication documentation reinforces that Active Directory remains foundational in many enterprise environments. (learn.microsoft.com) For security teams, the goal is not just convenience. It is consistency. Identity convergence helps ensure that access decisions are based on current status, not stale records. Why Active Directory still matters in modern access control Active Directory is still deeply embedded in enterprise infrastructure. Microsoft describes Active Directory as the directory many organizations use for core services and authentication. That matters because many access control environments still depend on legacy systems, on-premises services, or hybrid deployments. If your physical security stack, badge system, or facility workflow still depends on AD-linked identities, then identity convergence should respect that reality rather than trying to ignore it. The best approach is usually hybrid: keep Active Directory where it is still authoritative, connect downstream systems through supported integrations and standardized identity management practices, maintain consistent identity information across physical and digital environments. The role of enterprise identity management in unified access control Modern identity management platforms support standard protocols and identity integration patterns that are central to modern enterprise identity architecture. These platforms commonly support authentication, provisioning, directory synchronization, and federation across connected applications and services. That makes enterprise identity management useful for: authentication, provisioning, deprovisioning, directory synchronization, and federation across connected applications and services. For enterprise buyers, this is especially important when access control touches both IT systems and physical environments. You need a model that can scale across departments, locations, and vendors without multiplying administrative burden. Standard protocols make integration more secure and more scalable If you are building or evaluating an identity convergence strategy, the protocol layer matters. SCIM for provisioning and lifecycle automation SCIM is an open standard for exchanging identity data and automating user and group lifecycle operations between identity providers and connected applications. Microsoft Entra documentation similarly describes SCIM as a standardized way to synchronize user profiles and group data. SAML for federated enterprise sign-in SAML is a long-standing enterprise federation standard used to support secure authentication between identity providers and enterprise applications. OIDC for modern authentication OpenID Connect builds on OAuth 2.0 and is widely used for modern application authentication and single sign-on. The advantage of using standards is straightforward: you reduce custom connector complexity, improve portability, and make security architecture easier to maintain over time. What enterprise facility managers need from identity convergence Facility managers are often forced to operate in a world where physical access is managed separately from digital identity. That creates friction during: onboarding, role changes, temporary access needs, contractor access, after-hours access, and offboarding. Identity convergence helps facility teams work from the same lifecycle events that IT already uses. Instead of waiting on manual ticketing or email approvals, the organization can align identity status with access workflows more systematically. That is especially useful in multi-site commercial real estate environments, where inconsistent access rules across buildings or tenants can create both operational inefficiency and security exposure. What IT Directors and security teams should prioritize If you are responsible for the architecture, focus