Enterprise access environments are getting more complex, not less. IT teams, security operations, facility leaders, and property managers are expected to control who can enter buildings, systems, and sensitive spaces while also proving that those controls are consistently enforced. In that environment, audit-ready access is no longer a best practice — it is an operational requirement.
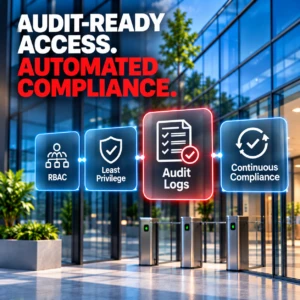
By 2027, organizations will need more than periodic reviews and spreadsheet-based access lists. They will need access governance automation that supports continuous compliance, produces reliable audit evidence, and reduces the manual burden on IT, security, and facilities teams. The core principles remain familiar: least privilege, role-based access control (RBAC), audit log management, and strong governance processes. What changes is the expectation that these controls should be embedded into daily operations, not added after the fact. (csrc.nist.gov)
Why Audit-Ready Access Matters Now
Audit readiness has traditionally been treated as a point-in-time event. Teams prepare evidence when a review, certification, or assessment is approaching, then move back to business as usual. That model creates risk because access permissions, contractor relationships, tenant needs, and staff responsibilities change constantly.
Modern compliance frameworks emphasize ongoing control over access and logging. NIST guidance supports access control based on policy, role, and least privilege, while CIS Controls v8.1 specifically calls for access control management and audit log management as core safeguards. ISO/IEC 27001 and ISO/IEC 27002 also frame access control as part of a broader information security management system. (tsapps.nist.gov)
For enterprise facilities and commercial real estate environments, that means the same governance discipline should apply across:
- employee badge access
- contractor and vendor access
- tenant-specific permissions
- privileged administrative access
- physical and logical access review processes
When these controls are fragmented, audit preparation becomes expensive and error-prone. When they are automated, organizations can improve oversight while reducing manual work.
What “Audit-Ready Access” Means in Practice
Audit-ready access is the ability to prove, at any moment, that access is:
- approved
- appropriate to the user’s role
- time-bound where needed
- logged
- reviewed
- revoked when no longer required
This is where identity governance and access governance automation become critical. A mature access program should not simply issue credentials. It should maintain an ongoing record of why access exists, who approved it, when it was last reviewed, and whether it still aligns with policy.
In practical terms, audit-ready access usually includes:
- Defined roles and entitlements
Access is mapped to job function, location, tenant, or operational need. - Least privilege enforcement
Users receive only the minimum access necessary to perform assigned tasks. NIST defines least privilege as restricting privileges to the minimum necessary to accomplish assigned tasks. (csrc.nist.gov) - Reviewable access decisions
Every approval, change, and revocation can be traced. - Audit logs and retention
Events can be reviewed to detect, understand, or recover from attacks or policy violations. CIS explicitly identifies audit log management as a core control. (cisecurity.org) - Governance workflows
Access changes follow standardized approvals, exceptions, and recertifications.
The 2027 Shift: From Periodic Reviews to Continuous Compliance
The biggest shift heading into 2027 is the move from reactive compliance to continuous compliance. This does not mean replacing human oversight. It means automating the repetitive parts of governance so people can focus on exceptions, investigations, and policy decisions.
Continuous compliance is especially important in environments where access changes quickly:
- seasonal staffing
- contractor rotation
- tenant turnover
- new facilities or sites
- hybrid work and remote administration
- temporary emergency access
Automation helps by standardizing the workflow around access requests, approvals, renewals, and revocations. It also helps teams detect drift — for example, when a user’s access no longer matches their role or when an inactive credential remains enabled.
Industry guidance supports this approach. CIS Control 6 focuses on managing access privileges, and CIS Control 8 focuses on collecting, alerting, reviewing, and retaining audit logs. NIST also emphasizes role-based and policy-driven access control. (cas.docs.cisecurity.org)
The Business Case for Access Governance Automation
For IT directors and enterprise security leaders, the value of automation is not just compliance. It is operational clarity.
1. Faster audit preparation
When access data, approvals, and logs are centralized, teams can produce evidence faster and with less manual reconciliation.
2. Lower risk of stale access
Automated recertification and expiration policies reduce the chance that old accounts or overprivileged users remain active.
3. Better accountability
RBAC and approval workflows make it easier to determine who approved what, when, and under which policy.
4. More consistent enforcement
Policies applied through workflows are less likely to vary by site, manager, or department.
5. Improved collaboration across teams
Facilities, security, IT, and property management can work from the same governance model instead of maintaining separate spreadsheets or siloed approval paths.
Key Components of an Audit-Ready Access Program
1. Role-Based Access Control
RBAC assigns access based on role rather than individual preference. NIST describes RBAC as a way to manage access based on job function, and it has long been recognized as a practical model for enterprise security. (csrc.nist.gov)
In commercial environments, RBAC can be used to separate:
- corporate administrators
- building operators
- tenant users
- contractors
- security personnel
- temporary visitors
2. Least Privilege Access
Least privilege is foundational. If a user only needs access to a subset of doors, applications, or administrative functions, they should not have broader privileges by default. NIST and CIS both support this principle as a core access control safeguard. (csrc.nist.gov)
3. Strong Audit Logging
Logs should capture access events, privilege changes, approvals, denials, and administrative actions. CIS Control 8 is explicit that audit logs should be collected, reviewed, and retained to help detect, understand, or recover from an attack. (cisecurity.org)
4. Access Review Workflows
A strong governance program requires regular access reviews. These reviews should verify:
- whether access is still needed
- whether the role has changed
- whether the user is still active
- whether any exceptions exist
- whether high-risk access requires additional approval
5. Separation of Duties
For sensitive environments, no single person should control every step of the process. NIST 800-171 discusses separation of duties, including ensuring personnel who administer access control functions do not also administer audit functions. (nvlpubs.nist.gov)
How Automation Supports Compliance and Governance
Automation is most effective when it supports, rather than replaces, policy. The goal is to make access governance measurable, repeatable, and easier to enforce.
Automated provisioning and deprovisioning
When a person changes roles or leaves the organization, access should update automatically wherever possible. This reduces the risk of lingering permissions.
Time-bound access for contractors and visitors
Temporary access should expire by default. Renewal should require re-approval.
Policy-based approvals
Requests can route to the right approver based on site, role, privilege level, or tenant relationship.
Continuous recertification
Instead of annual-only reviews, organizations can trigger more frequent reviews for privileged, sensitive, or exceptional access.
Evidence generation
Automation can help assemble the audit trail required for internal reviews and external assessments.
Common Gaps That Create Audit Risk
Many organizations believe they are “covered” because they have an access control policy. The problem is execution.
Common gaps include:
- inconsistent role definitions across sites
- duplicate accounts
- shared credentials
- manual approval chains that are not documented
- stale contractor access
- weak logging retention
- no evidence of periodic reviews
- exceptions managed by email instead of workflow
- physical access and digital access governed in separate systems
These are exactly the kinds of issues that make audits harder and more disruptive. They also make it difficult to demonstrate that access is controlled according to policy, role, and business need.
What Enterprise Teams Should Prioritize in 2027
For IT Directors
Focus on identity governance, privileged access review, log retention, and integration with broader security operations.
For Enterprise Facility Managers
Standardize credential issuance, visitor access, contractor time limits, and site-level approval workflows.
For Commercial Property Owners and CRE Property Managers
Create consistent access rules across properties while supporting tenant-specific requirements and lease-driven exceptions.
For Security Operations Teams
Centralize audit logs, investigate anomalies faster, and ensure access changes are visible in the same operational environment as other security events.
How to Evaluate Whether Your Access Program Is Audit-Ready
Ask these questions:
- Can we show who has access right now?
- Can we explain why each access permission exists?
- Can we prove when access was approved?
- Can we demonstrate least privilege?
- Are logs retained and searchable?
- Do access reviews happen on a defined schedule?
- Are temporary credentials automatically revoked?
- Can we trace exceptions back to an approver?
- Are physical and digital access controls aligned?
If any of those answers are unclear, the program is not yet truly audit-ready.
Building Toward a More Governed 2027
The future of access governance is not about adding more manual checks. It is about making the controls themselves easier to operate, verify, and audit.
Organizations that succeed will be the ones that treat access as a governed lifecycle:
- request
- approval
- provisioning
- usage
- review
- renewal
- revocation
- retention of evidence
That lifecycle should be supported by automation, but directed by policy. That is the difference between simply managing access and building an audit-ready access program.
Conclusion
Audit-ready access in 2027 will depend on a simple but demanding formula: automate the workflow, enforce least privilege, maintain strong logs, and connect access decisions to clear governance rules. Standards and controls from NIST, CIS, and ISO all point in the same direction: organizations need structured, reviewable, and policy-driven access management. (csrc.nist.gov)
Millennium is a scalable, hosted, access control platform that services any type of real estate. Our cloud-based solution allows managers and tenants to efficiently manage their physical security from anywhere while enhancing experience and driving profitability.