The SMB Access Gap: Enterprise Security Without the IT Department
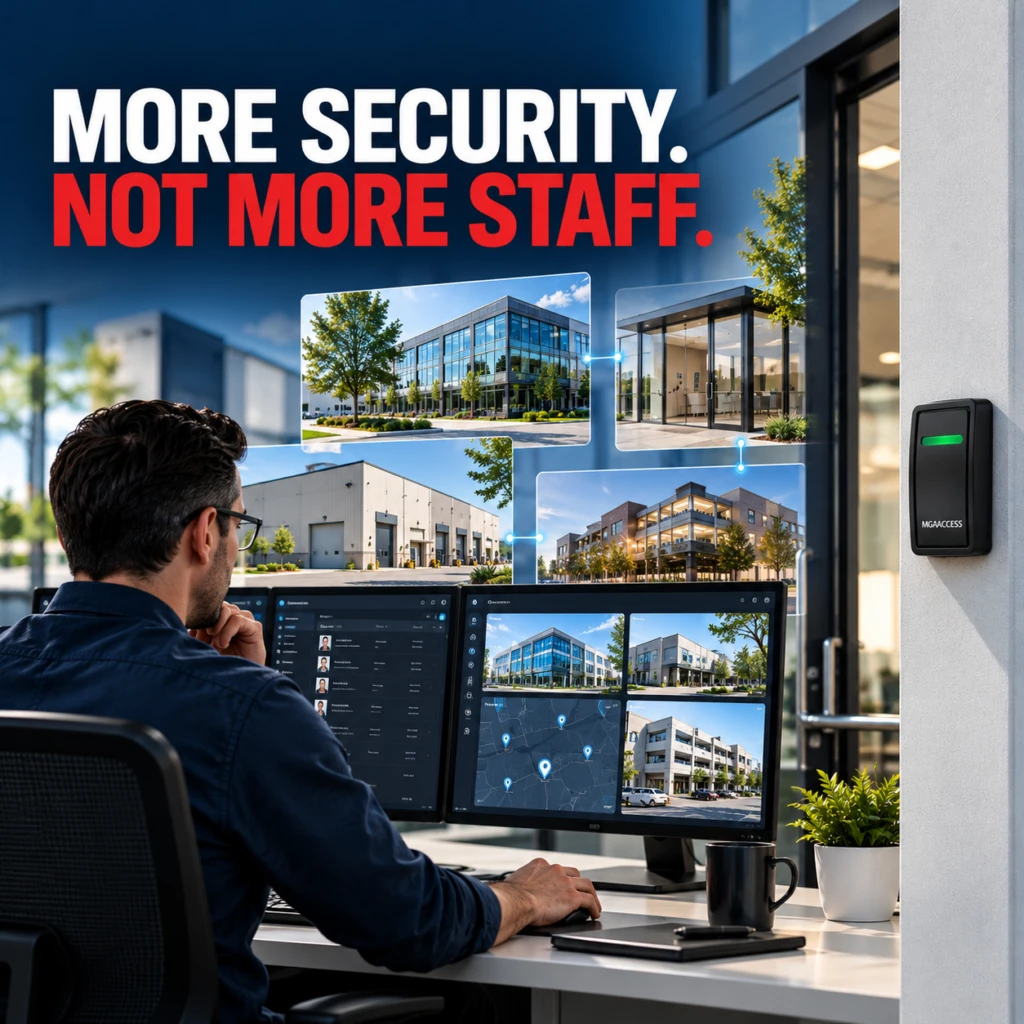
Enterprise security has a blind spot. For too many organizations, access control still depends on manual processes, disconnected systems, and overworked teams. That might have been manageable when one site, one badge system, and one administrator could cover everything. It is not manageable now. Today, IT Directors, Facility Managers, CRE Property Managers, Commercial Property Owners, and Security Operations teams are expected to support more users, more locations, more exceptions, and more risk — often without the staff to keep up. That is the SMB access gap. It is the gap between the security posture your organization needs and the operational reality your team has to work with. And it is exactly where enterprise security starts to break down. What the SMB Access Gap Really Means The SMB access gap is not just a staffing issue. It is a security architecture issue. When access decisions depend on manual approvals, inconsistent badge rules, siloed systems, or outdated policies, the result is predictable: too much access, too little visibility, slow revocation, weak auditability, and unnecessary exposure across people, places, and systems. That is a serious problem for lean organizations and distributed enterprises alike. It is especially risky in commercial properties and multi-site environments, where access often has to be managed across tenants, vendors, contractors, employees, and visitors. If your team is still forced to patch together access control with spreadsheets, email approvals, or legacy tools that were never built for modern governance, you are already carrying security debt. Why Enterprise Security Is Harder Without a Large IT Department Modern access control is no longer just about opening a door. It is about proving identity, enforcing policy, limiting privilege, and creating an audit trail that holds up under scrutiny. That is a lot to ask of a small team if the system was never designed to scale. The pressure usually shows up in a few familiar ways: Manual provisioning slows everything down Every new employee, contractor, or tenant request creates work. Every role change creates more work. Every offboarding event creates risk if it is not handled immediately. Siloed systems create inconsistency If physical access, identity management, and security operations live in separate places, policies drift. What is allowed in one building may not match another. What is revoked in one system may still be active in another. Visibility disappears across sites Without centralized control, it becomes difficult to answer basic questions: Who has access? To what? For how long? And under what policy? Legacy tools demand too much maintenance Older systems may still function, but they often require heavy administration, on-prem support, or workarounds that drain time from already stretched teams. Physical and digital access are no longer separate problems The modern enterprise has a cyber-physical security challenge. If identity governance is weak, physical access becomes weak. If authorization is unclear, security becomes inconsistent. That is why the SMB access gap matters. It is not just about convenience. It is about control. The Security Model That Closes the Gap The answer is not more complexity. The answer is a smarter access model built around identity, least privilege, centralized policy, and zero trust principles. That starts with one core assumption: access should never be granted simply because someone is “inside” the network, inside the building, or inside the organization. Access must be verified, limited, and continuously governed. Zero trust access control Zero trust is not a product. It is a security approach. Instead of assuming trust based on location or legacy boundaries, zero trust evaluates identity, context, and policy before access is granted. That applies to digital systems, and it increasingly applies to physical access as well. For lean teams, this matters because it shifts the model from reactive administration to governed access. The system is doing more of the work, so the team does not have to. Identity-based access control The cleanest way to scale access is to tie it to identity. That means access follows the person, not the spreadsheet. It follows role, not memory. It follows policy, not improvisation. Identity-based access control gives organizations a more reliable way to manage permissions across buildings, departments, sites, and user types. Least privilege by default If someone does not need access, they should not have it. That principle sounds simple, but it is one of the most effective ways to reduce risk. The fewer unnecessary permissions you carry, the smaller your exposure when something goes wrong. Role-based access control Role-based access control helps reduce administrative burden by grouping permissions according to job function or user category. For example: facility staff may need broad operational access, contractors may need limited, time-bound access, tenants may need access only to designated areas, executives may need elevated access to specific spaces. The point is not to overcomplicate access. The point is to make it predictable, repeatable, and enforceable. What Modern Access Control Should Look Like If your organization wants enterprise security without enterprise staffing, your access model should do five things well: 1. Centralize policy Security teams should not have to manage access rules separately for every site or department. Policy should be governed from one place. 2. Reduce manual intervention The fewer handoffs required to grant, adjust, or revoke access, the less room there is for error. 3. Support the full user lifecycle Access should be easy to assign when someone joins, update when their role changes, and remove immediately when they leave. 4. Create audit-ready visibility Security operations teams need clear logs and consistent records. If you cannot prove who had access and why, you do not really have control. 5. Scale across physical and operational environments Access control should work across office buildings, mixed-use properties, distributed teams, and evolving portfolios without forcing your staff into constant cleanup mode. That is the difference between a system that looks modern and a system that actually reduces risk. Where Commercial Property and CRE Teams Feel the Pain Most In commercial real estate and property management, access control complexity is often underestimated. You are not just managing employees.